Tredy Platform
The assurance control plane
One system that runs the recurring mandatory work, keeps the rule set it produces, and enforces that rule set on every action — human or agent — before it lands.
Book a demo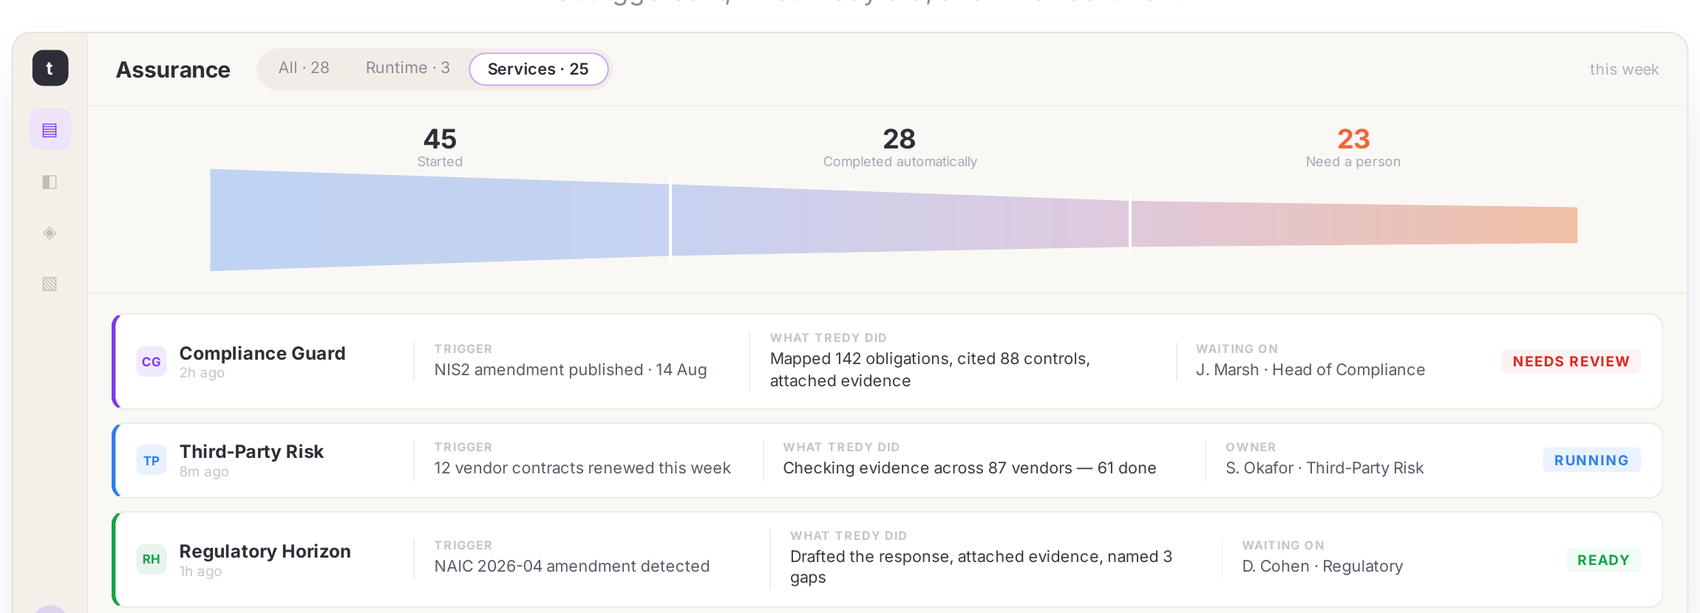
Assurance services
Run the work
end to end.
The recurring mandatory work — regulatory change, third-party risk, policy sign-off, resilience testing — installed as a service with an owner and a deliverable.
- Starts on the event. A circular publishes, a certificate lapses, a control fails.
- Maps the obligations, cites the controls and attaches the evidence.
- Escalates only what needs judgement, to a named owner.
- Delivers a response pack, an approval trail or an evidence file — not a dashboard.
- Encoded from best practice, then tuned to your thresholds and escalation paths.
The rule set
Set the rules once.
Everything reads them.
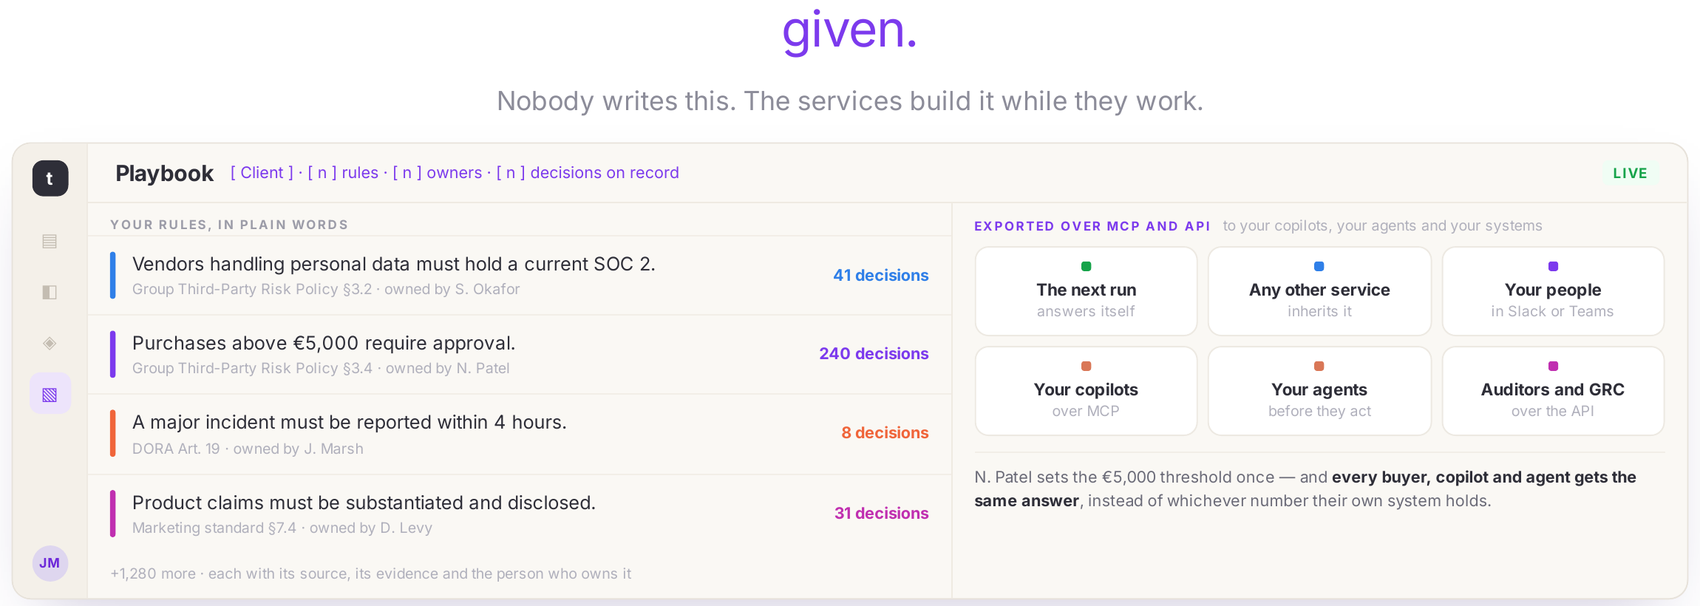
Every obligation from your policies, regulations and contracts, in plain words — produced by the work rather than authored by hand.
- Each rule carries its source, its version and the person who owns it.
- Written by a run, not a person — 0 rules without a source.
- Exported over MCP and the REST API to copilots, agents and enterprise systems.
- Your people ask it in Slack or Teams and get the same answer.
- Auditors and GRC pull it with the evidence attached.
Runtime assurance
Stop it before
it lands.
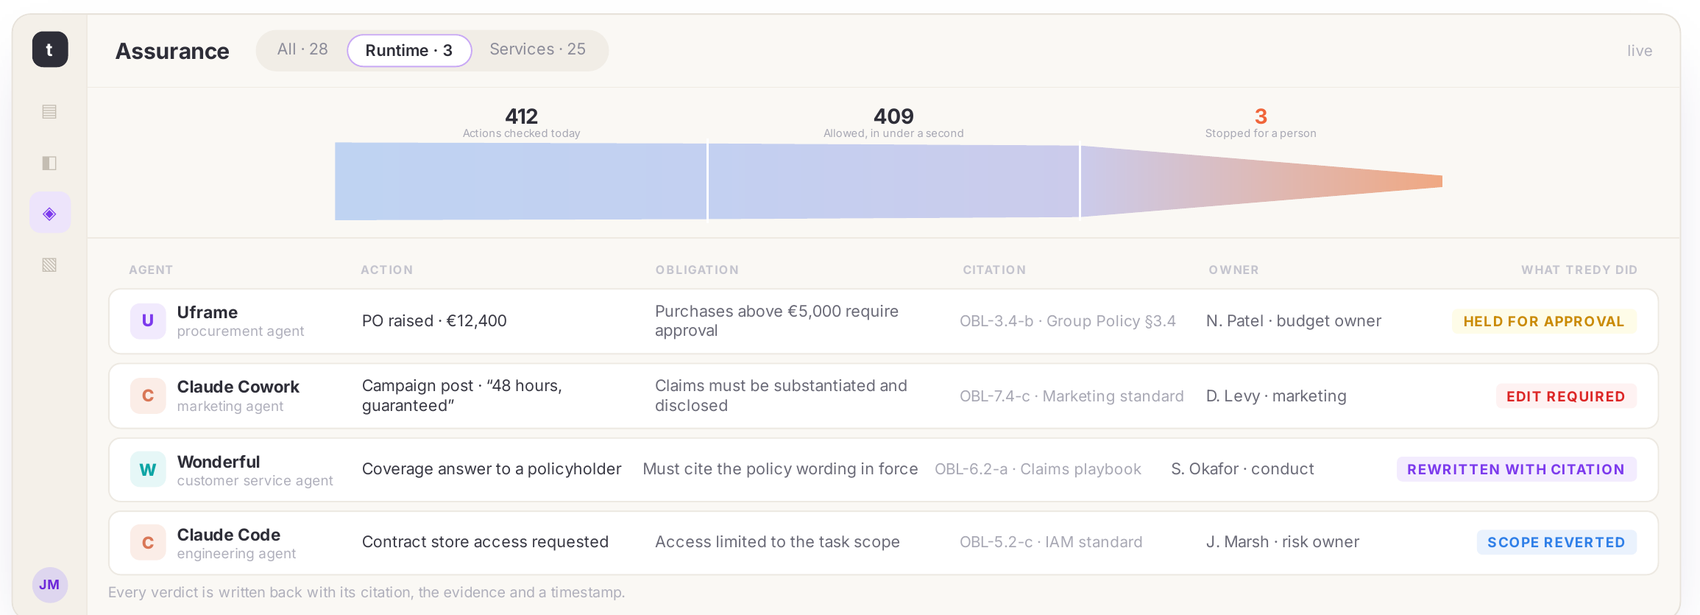
Every consequential action, by a person or an agent, checked against the same rule set before it runs — malicious or mistaken.
- Allow, escalate, advise or block. Safe actions clear in under a second.
- Covers your systems, your agents and the endpoint where a file gets deleted.
- What cannot clear goes to one named owner, with an SLA.
- Deterministic checks — the rule that fired can always be shown.
- First enterprise rollout next quarter.
Evidence and audit
Prove it,
years later.
Every verdict is written back with the rule that fired, the evidence behind it and a timestamp — so an examiner can be shown the working.
- The decision, its rationale and its owner, dated and on the record.
- The rule version in force at the moment of the action.
- Fuzzy inference and deterministic rules, not an LLM verdict — inspectable and replayable.
- Approved decisions return to the rule set, so the next run costs less.
- Mapped to DORA, EU AI Act, NIS2, ISO 42001 and NIST AI RMF.
What starts the work
Six kinds of change. One runtime.
Assurance work is not scheduled, it is triggered. Something changes in a system you already run, and the service that answers for it starts.
Third parties
A vendor changes, evidence expires, or a new dependency appears.
Vendor Onboarding
Regulatory & legal
A new requirement affects products, policies, or controls.
Regulatory Response · Regulatory Horizon
Cyber & resilience
A threat, incident, or recovery condition changes exposure.
ITSCM & SaaS DR Testing
Controls & process
A control fails, evidence is missing, or an exception persists.
Policy Lifecycle Assurance
Technology & AI
A model, system, data flow, or intended use changes.
Your own service
Operations & people
Ownership, access, process, or operating conditions change.
Your own service
What happens next
The same six steps, every time.
- 01
Event detected
A material change enters from a connected system.
- 02
Applicability determined
Context and rules establish what the event requires.
- 03
Service activated
The relevant governed assurance service begins work.
- 04
Work completed
Evidence is gathered, tested and assembled.
- 05
Owner engaged
Only judgement, exceptions or approval interrupt the owner.
- 06
Outcome approved
The decision and evidence trace become reusable practice.
One rule set, and nobody wrote it
Every obligation your company runs on, produced by the assurance work rather than authored by hand — each with its source, its evidence and a named owner.
Illustrative
Live in four weeks. Yours from there.
Tredy meets you where your data already is.
One control plane
Services, the rule set and runtime enforcement in a single system, not three tools stitched together.
Your environment
Deployed in your VPC, as PaaS or as SaaS. Nothing leaves your tenant, and you keep the rule set.
Connects to what you run
Slack, Teams, Microsoft 365, Google Workspace, Jira, Confluence, ServiceNow — over MCP and the REST API.
Start with one service.
A 30-minute scoping session with your risk owner and your IT contact. We leave with the first service named, the connections listed, and a date.