Governing AI and human actions across the tools your teams already use
- Claude
- ChatGPT
- Slack
- Microsoft Teams
- Microsoft 365
- Gmail
- GitHub
- GitLab
What it does
- Regulatory Response — Continuous, cited evidence for SEC disclosure, SOX internal controls and EU AI Act requirements.
- Evidence — Reconstruct any action across your stack, for audit committees and for regulators.
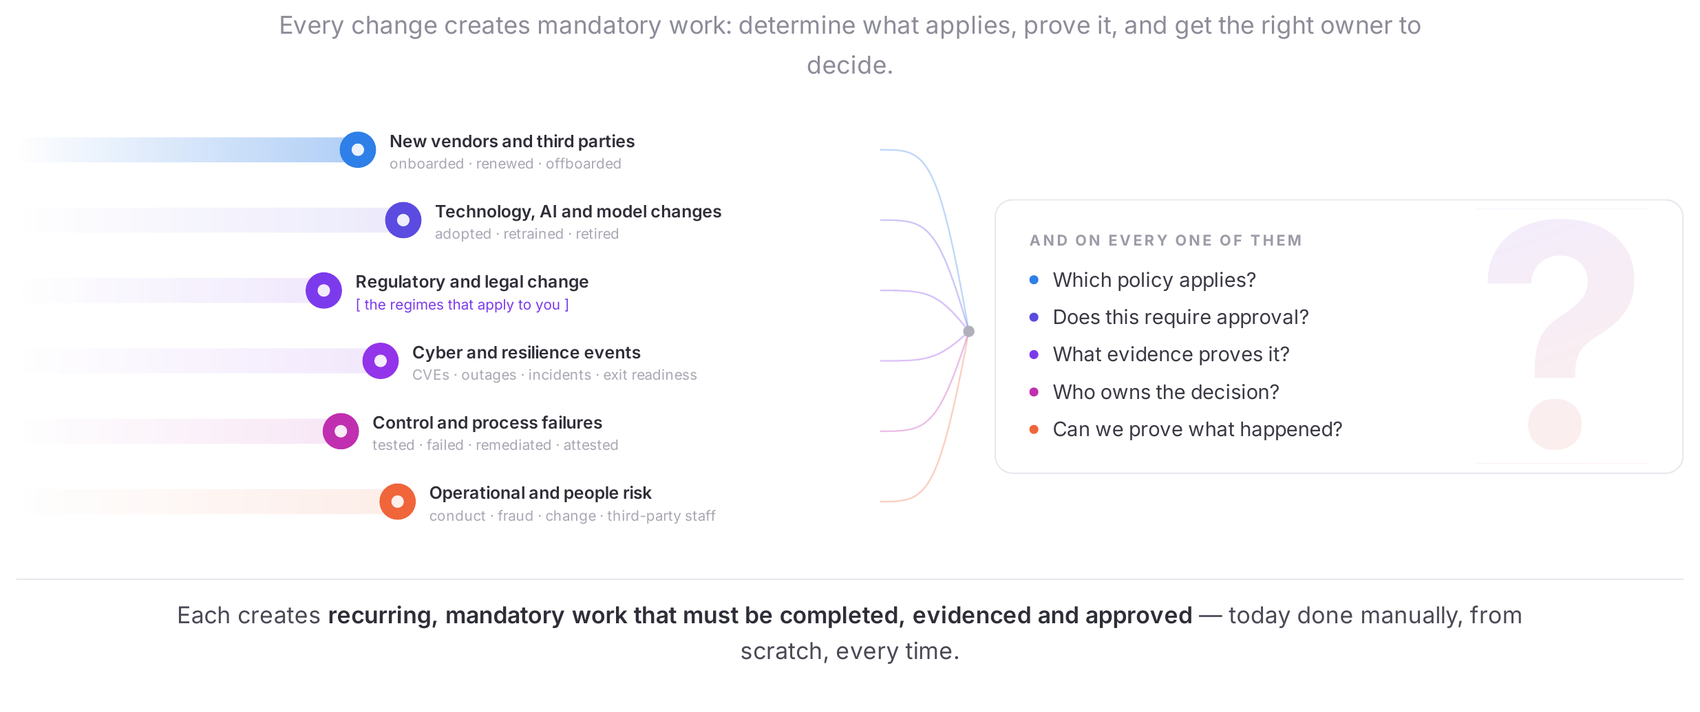
- One rule set — Disclosure controls, internal controls and AI governance answer from the same policy.
What gets in the way
Board-level technology oversight obligations
Directors are personally liable for technology governance failures. They need clear dashboards and evidence of oversight — not technical jargon they can't act on.
SEC disclosure requirements for technology risk
Public companies must disclose material technology risks. Without systematic tracking of decisions and outcomes across your stack, you can't report what you can't measure.
Shareholder scrutiny on technology spending
Investors want to see technology ROI. Proxy advisors are starting to score governance practices. The gap between technology spend and demonstrable returns creates activism risk.
Audit committee technology governance gaps
Audit committees are responsible for technology-related internal controls. Current audit frameworks weren't designed for complex, interconnected stacks with autonomous systems.
Start with one service.
A 30-minute scoping session with your risk owner and your IT contact.